000° Security and GDPR
Your customers’ data stays in a safe harbour, in Europe.
This page sets out exactly what we do with the data you trust us with: where it is stored, who can see it, how emails are sent and how your customers exercise their rights. No certificates we don’t have, no vague promises.
045° Where data is stored
In the European Union. All of it.
The app, the database and our sending server are hosted by OVHcloud, in France. Your customers’ names, addresses and orders never leave the EU and never pass through an American email provider.
090° How we send
We protect every customer’s reputation, including yours.
Many shops’ emails leave from our sending server. If just one of them sends spam, Gmail and Yahoo start blocking all of us. That is why the rules below are the same for everyone and are not up for negotiation.
- Our own sending server
Our own server, hosted by OVHcloud in France. We do not rent sending from an American provider.
- Your domain, authenticated
We prepare SPF, DKIM and DMARC for your shop’s domain and regularly check that the records are still in place.
- DKIM keys in a vault
The private signing keys are kept in a separate secrets vault, never in the database.
- One-click unsubscribe
Every marketing email has one-click unsubscribe, following the RFC 8058 standard required by Gmail and Yahoo.
- The suppression list
An address that bounced or clicked “spam” gets nothing more. The list stays even after you delete the contact.
- A daily limit earned by behaviour
Every account starts with a low limit, which doubles as long as the figures stay clean. It does not grow with how much you pay.
When we stop sending
We only judge an account’s figures after at least 200 emails, so that two bounces out of ten do not lead to the wrong conclusion.
| Signal | Limit stops growing above | Sending stops above |
|---|---|---|
| Spam complaints | 0.1% | 0.3%, the threshold Gmail and Yahoo publicly require |
| Hard-bounced addresses | 2% | 5%: the list needs cleaning |
135° How we protect data
What you give us once never appears again.
- Your shop’s keys, encrypted
Your shop’s API keys and other access details are stored encrypted. Once you save them, we never show them again, not in the interface and not in logs.
- An audit log that cannot be deleted
Who changed what, when and from which IP address. The log is append-only: it cannot be edited or deleted, not even by us from the app.
- Team roles
Owner, Admin and Member. Only the first two can create API keys and webhooks.
- API keys with separate permissions
Each key gets only the permission it needs, has its own rate limit and can be revoked at any time.
- Payments through Stripe
You enter your card details directly with Stripe. They never reach Azimea’s servers.
180° Your customers’ rights
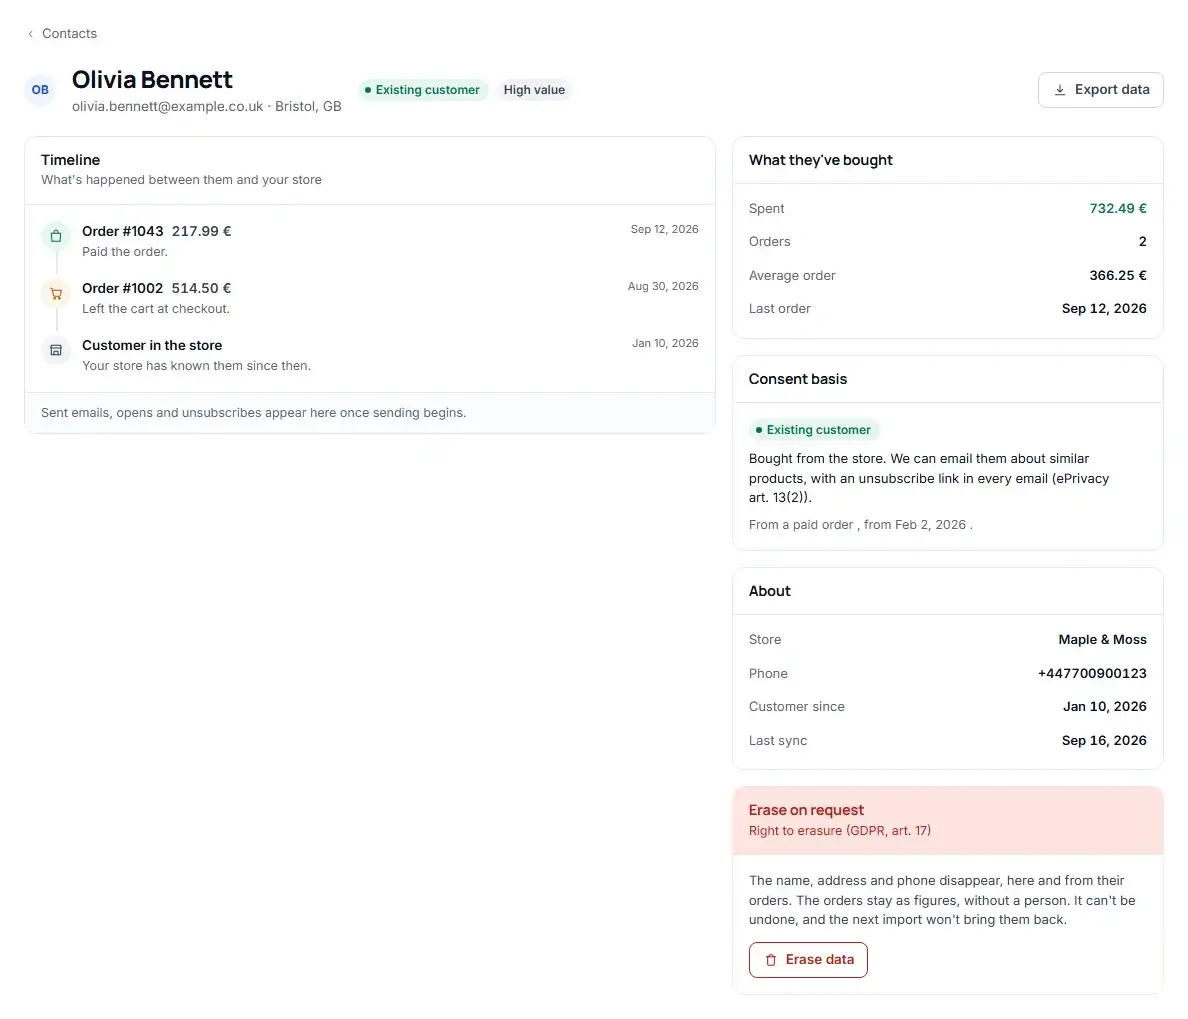
When a customer asks for their data, one button does it.
You are the data controller; we are the processor. Azimea gives you the tools to answer a GDPR request in minutes, not days.
- Erasure on request (Art. 17). The person’s name, address and phone number disappear from every module. Orders remain as figures, with no person attached, and the next import does not bring them back.
- Export (Arts. 15 and 20). Download everything we know about a contact, in one file.
- The legal basis, for every contact. You know why you may email them: consent or existing customer, since when and from where.
- Limited retention. After 400 days, sent emails lose the recipient’s address and their content. Only the numbers remain, for reports.
225° Subprocessors
Who else touches the data. The full list.
We keep the list up to date and tell you by email before we add or change a subprocessor, so you have time to object.
| Provider | What for | What data it receives | Where |
|---|---|---|---|
| OVHcloud | Hosting the app and the database, the sending server | Your account data and your shop’s customer data | France (EU) |
| Stripe Payments Europe | Subscription payments | Your company’s billing details. You enter your card directly with Stripe. | Ireland (EU) |
| [to be completed before launch] | — | — | — |
Last updated: [date].
Data processing agreement (DPA)
Article 28 of the GDPR requires a contract between you and us for your customers’ data. We send you the DPA on request, filled in with your company’s details, ready to sign.
Acceptable use policy
No bought, rented or scraped lists. No emails to people who have not given you consent or bought from you. No misleading subject lines and no hidden unsubscribe. Above 0.3% complaints, sending stops automatically.
Read the full policy315° Questions
What shop owners ask us about data.
Have another question, or does your accountant or lawyer need something specific? Write to us at suport@azimea.com.
Where is my customers’ data stored?
At OVHcloud, in France. The app, the database and the sending server are all there. Your customers’ data never leaves the European Union.
Do I need to sign a DPA with you?
Yes, the GDPR requires it, because we process your customers’ data on your behalf. Write to us at suport@azimea.com and we will send you the completed DPA, ready to sign.
Can I email customers who did not tick the newsletter box?
You can email people who have bought from you about similar products, with an unsubscribe link in every email (ePrivacy Directive, Art. 13(2)). Azimea records, for every contact, the basis on which you email them. For anything else, you need their consent.
Why might sending from my account be stopped?
If more than 0.3% of recipients mark your emails as spam, or more than 5% of addresses bounce them. The account then goes into quarantine and a person on our team restarts it, once we have talked to you. You will see the reason in the app.
Are you ISO 27001 or SOC 2 certified?
No, not yet. We are a small, new company. Instead of a badge, this page shows you what we actually do, and if you need details for an audit, we will give them to you in writing.
000° Start today
Emails that bring orders, from a server in Europe.
14 days free, counted from the day you connect your shop. No card needed.